Trust and Responsibility Rooted in Strong Corporate Governance
A robust governance framework at CAMS lays the foundation for accountability, transparency and ethics throughout the organisation, protecting stakeholders interest at all times and fostering long-term value creation.
Reinforcing a Robust Governance Framework
A well-established system of responsible practices and policies drives sustainable operations and business conduct at CAMS, in alignment with the compliance and regulatory requirements. Implemented by the Board and overseen by various Board Committees, the framework reinforces our commitment to the highest level of governance, maximising stakeholder trust and further solidifying our value proposition. Our adherence to country-specific laws and regulations, combined with a diverse and independent Board, strengthens oversight and fosters a more resilient and effective governance structure.
Integrity at the Core
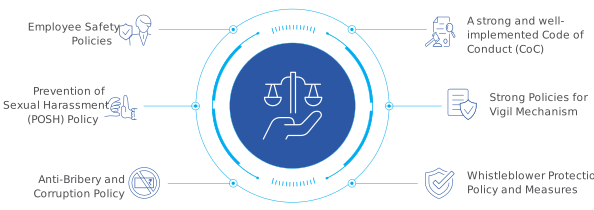
At the heart of our corporate governance policy is our unwavering dedication to ethical conduct and decision-making and the highest level of integrity. This is enabled by encouraging doing what is right, along with responsible leadership and strong policies, enforced through well-structured governance mechanisms. Illegal or unethical practices, if any, are reported and addressed promptly through a robust vigil mechanism and various other policies and measures.
Advancing Cybersecurity Resilience
As the largest RTA and leading financial provider, CAMS handles enormous volumes of sensitive data. Recognising this and the potential financial, reputational and legal risks associated with it, we continuously invest in strengthening our data security and advancing cyber resilience. With a comprehensive Information Security Management System, supported by robust cybersecurity and data privacy policies, periodic audits and reviews, and constant oversight by various Committees, we are building a secure, resilient and trusted digital ecosystem.
- ISO 27001 certified
- Robust policies on cyber security, cyber resilience, and data privacy
- Periodic review of Auditor's Report by the Audit Committee to oversee policy implementation measures and procedures
- Periodic review of the cyber security system by the Risk Management Committee, IT Strategy Committee and IT Committee
Board Committees
- Audit Committee
- Stakeholders' Relationship Committee
- CSR and ESG Committee
- IT Strategy Committee
- Nomination and Remuneration Committee
- Risk Management Committee